Image

Bogen Communications is actively assessing the recently disclosed global exposure to PHP vulnerabilities and their potential impact on Nyquist systems. This page will be updated as additional information and customer guidance become available.
Summary
In October 2026, two critical security vulnerabilities were discovered in PHP, a widely used programming language used throughout the world. If exploited, these vulnerabilities could allow remote attackers to execute malicious code on affected systems. This is a global cybersecurity issue impacting systems that use vulnerable PHP components.
Affected Nyquist Products and Solutions
Bogen is actively investigating the impact of CVE-2026-109618 and CVE-2026-109619 on Nyquist software and hardware appliances. We will provide updates as more information becomes available.
Official Updates from Bogen Communications:
October 26th, 2026: 3:00pm
Customers on Nyquist Versions 10 and 11 software can apply the security update utilizing the Technical Service Bulletin process. It is a “button-click” process that will update the Debian OS components, including the updated PHP package.
If the Nyquist solution is running on an older release that cannot be fixed via the Debian update as stated, and/or if the system is unable to update the Nyquist server to the latest Nyquist release, Bogen recommends that the Nyquist server not have Internet connectivity until able to perform a Nyquist update and subsequent Debian update.
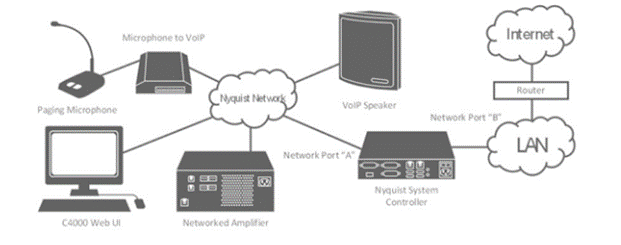
Nyquist should be isolated from any untrusted network access. If the server must remain connected, access to the Nyquist server should be restricted through properly configured firewall rules to only known, trusted IP addresses. This mitigation should be implemented and validated by the customer's IT or network security team.
Port A and Port B Configuration
Network Gateway and NTP Configuration
The gateway setting must not be removed or left unset. Nyquist appliances require a valid gateway IP address for multicast operation.
To reduce Internet exposure, do not configure Nyquist appliances to use Internet-based NTP servers. This recommendation applies to both standalone appliances and appliances operating with a Nyquist server.
Use one of the following configurations:
1. Use the Nyquist server for NTP
2. Use an NTP server on the local network segment
3. Use an NTP server on the customer's internal network
Important: Do not configure Nyquist appliances to use external, Internet-based NTP servers. Doing so typically requires configuring the appliance with a gateway that provides a route to the Internet, increasing unnecessary network exposure.
October 23, 2026: 4:00pm
Bogen’s Technical Service Bulletins (TSBs) regarding the PHP2SHELL vulnerability are now available.
Nyquist C4000 Customers: Critical PHP Security Response #TSB-C4-2026-08. This patch can also be found via the Nyquist C4000 Resources webpage.
Bogen ES Dealers: Visit the ES Dealer Resources webpage through your Bogen ES Dealer Portal to access the E7000 Technical Service Bulletin.
We will continue to update this page as additional information becomes available. Thank you for your patience as we work through this issue.
October 23, 2026: 11:52am
Bogen is aware of the widely reported PHP2SHELL vulnerability, a global cybersecurity issue that may affect Nyquist systems.
We are actively evaluating the situation and developing our response. Addressing this issue will require an upgrade to Nyquist E7000 software versions 10 or 11 or C4000 software versions 7 or 11.
We are working to finalize the technical details and upgrade requirements. Additional information will be provided by 4pm EST today.
We appreciate your patience as we work to address this issue and provide customers with clear guidance on next steps.